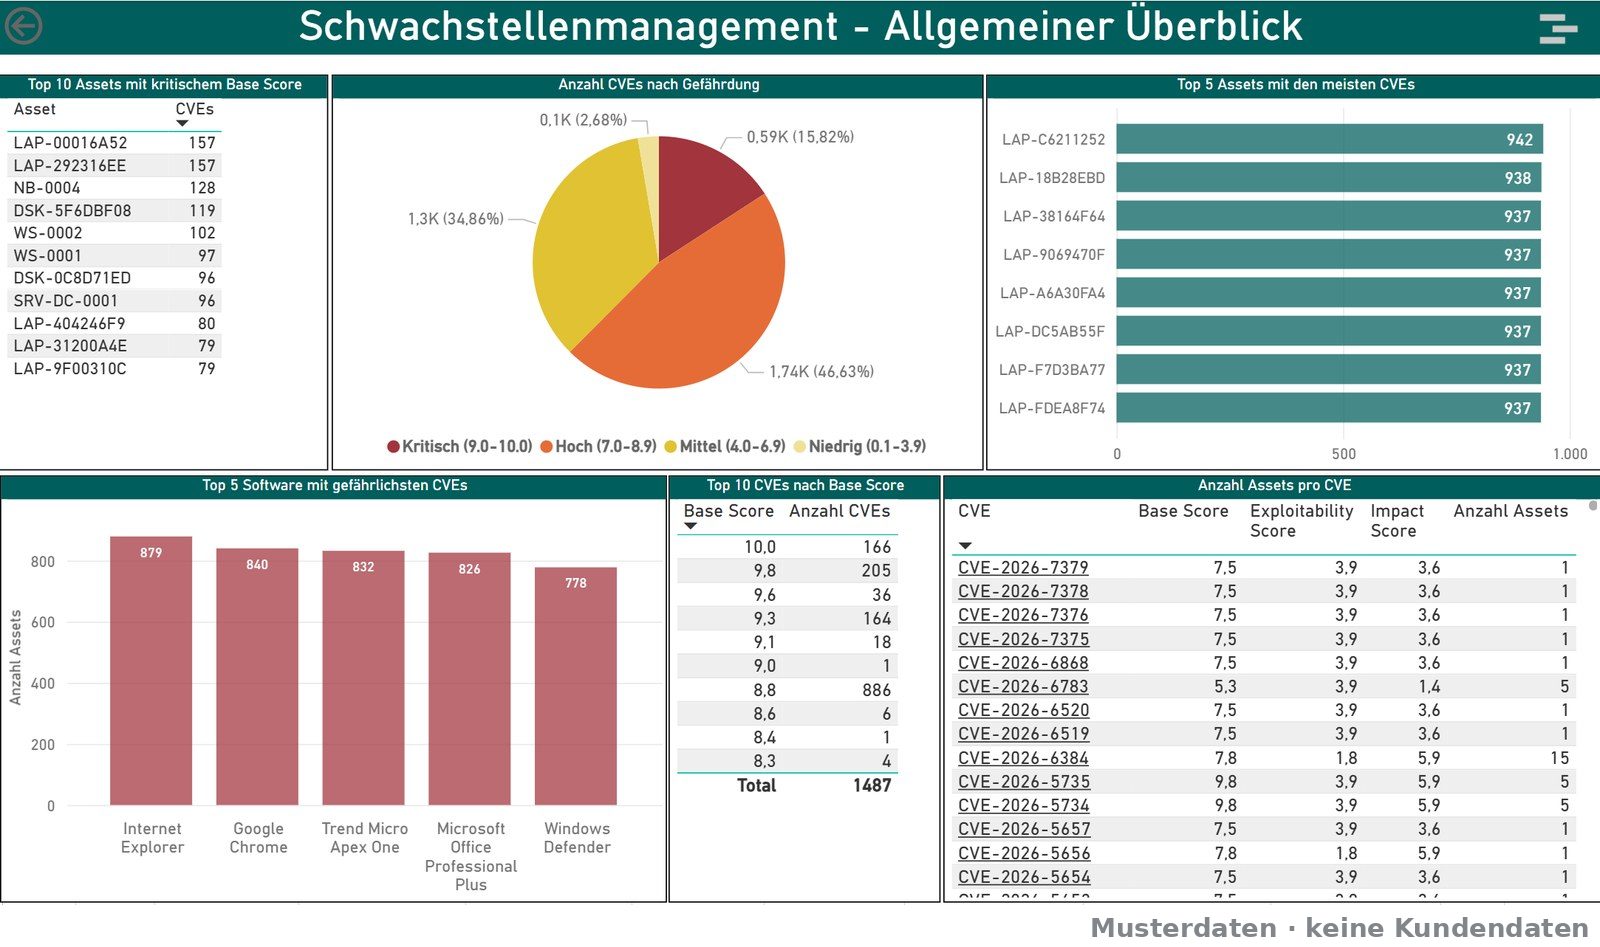
Advisory Integrated uses inventory data from the Deskcenter Management Suite to match installed software products and versions with known vulnerabilities from the National Vulnerability Database (NVD). The included Power BI dashboards show CVE severity, potentially affected devices and software products, and historical vulnerability trends.
Features
- Identify: match known CVEs to inventoried products and versions, based on the NVD.
- Assess: review CVSS base, exploitability and impact scores.
- Prioritise: highlight devices and software requiring attention.
- Report: use dashboards and historical trends to support documentation.
- Software lifecycle: make products without vendor support and outdated versions visible.
Remediation through the Deskcenter Management Suite
Advisory Integrated identifies and assesses. Remediation is performed separately through the software deployment and patch management capabilities of the Deskcenter Management Suite, subject to the modules in use. Advisory does not initiate patches directly.
Good to know
Advisory is not an active network or application scanner; matching is based on inventory data. These insights can support security risk management and documentation relating to NIS2, critical infrastructure requirements (KRITIS), DORA and ISO/IEC 27001 where applicable. They do not replace an ISMS or other required security measures.
Using an inventory system from another vendor? mosaic Advisory Connect →